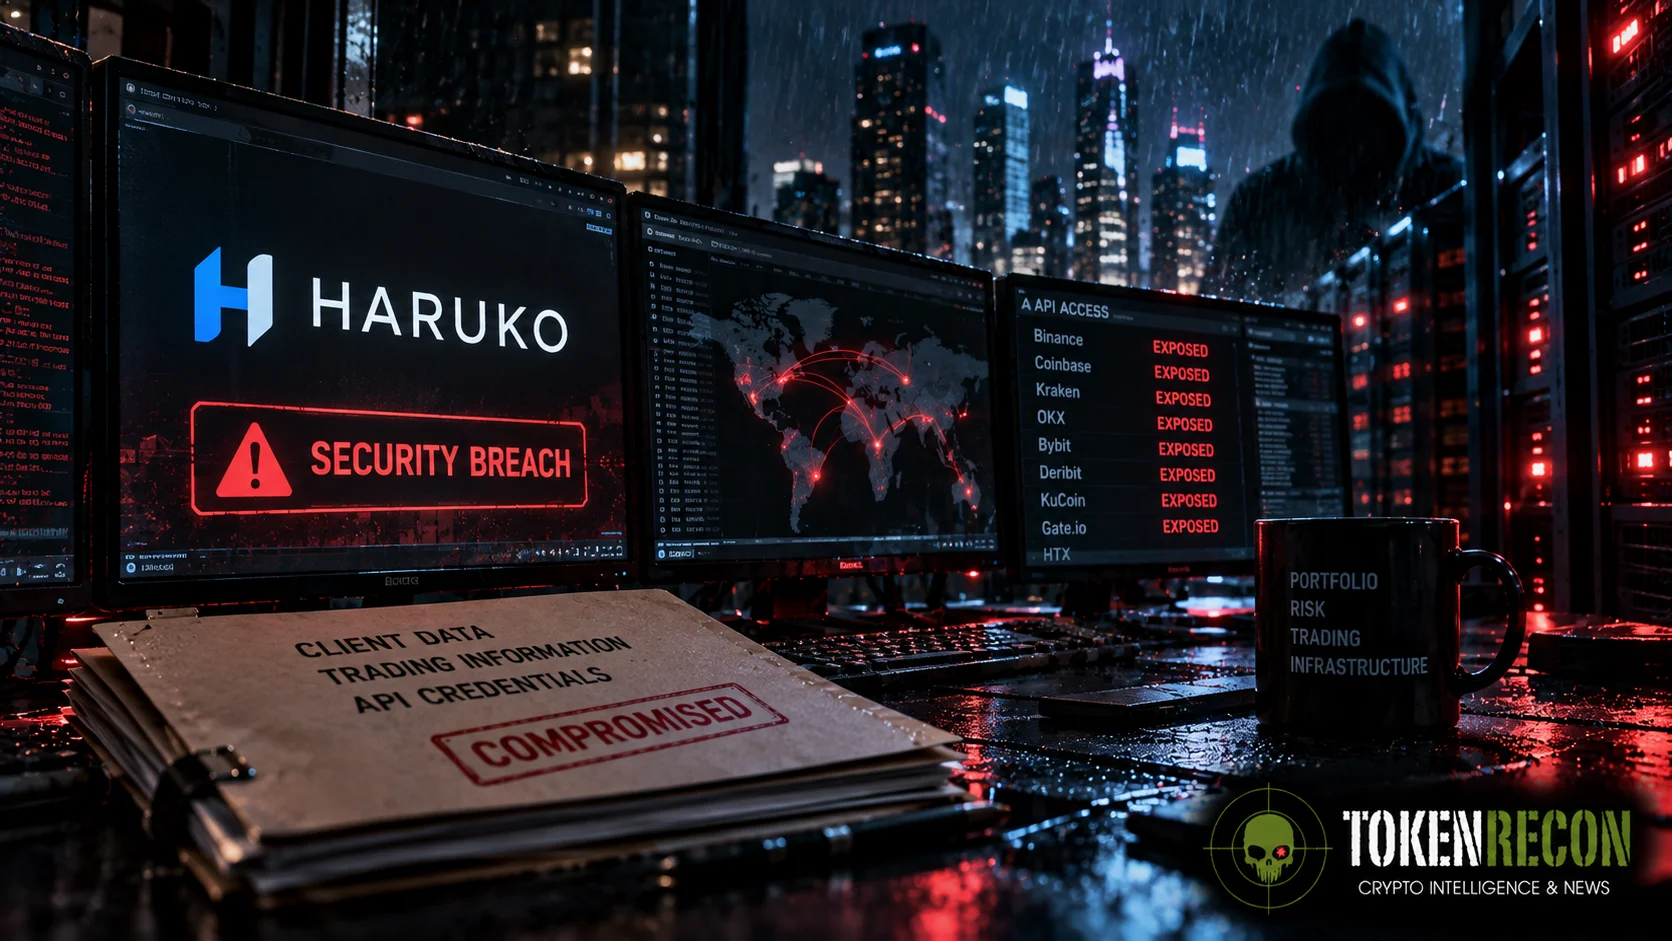
Digital-asset technology provider Haruko has suffered a targeted cyberattack affecting 15 institutional clients, exposing exchange API information and confidential trading data.
Haruko provides portfolio, risk and treasury-management infrastructure connecting hedge funds and other professional firms with centralized exchanges and onchain protocols.
The compromised exchange credentials were described as read-only, but sources told CoinDesk that several smaller clients with weaker account controls may nevertheless have lost limited amounts of cryptocurrency.
An attacker who obtains trading and portfolio data can identify positions, exchange relationships and operational routines even without gaining direct withdrawal authority. That information can support targeted phishing, market manipulation or follow-on attacks against individual clients.
Haruko says it has closed the vulnerability, refreshed server-side secrets and engaged outside specialists to investigate. The company has not publicly disclosed the intrusion method, total losses or complete timeline.
Institutions using connected portfolio systems should review API permissions, revoke and recreate affected credentials, check exchange logs and confirm that withdrawal addresses and multifactor-authentication settings remain unchanged.
TOKEN RECON ASSESSMENT
This incident demonstrates that “read-only” access is not automatically harmless.
Trading data can reveal strategy, exposure and infrastructure. API configurations can also become dangerous when combined with weaknesses in a client’s exchange-account controls.
Watch Haruko’s root-cause report, confirmed financial losses, client notifications and whether the stolen information is used in follow-on attacks.
Sources
CoinDesk. Haruko attack affects 15 institutional clients